NIST 800-53 Controls, Implemented Right
Expert NIST SP 800-53 implementation for federal contractors and security-minded companies. We select your baseline, build the controls and keep evidence assessment-ready.
The Control Catalog Behind Federal Security
NIST SP 800-53 is the federal catalog of security and privacy controls and the foundation of FISMA and FedRAMP programs.
Trusted by market leading technology companies




Workstreet has been a true partner. They embedded security into our daily workflow, took on the heavy lifting, and enabled us to move faster by unblocking security reviews without draining our team.


All of them (security reviews) have been super smooth for us to get through because of the work that you guys did for us. We've had no hiccups, no issues, passed everything. And it's been great.

Workstreet helps us move a lot faster. I save time, our engineers save time, and we’re able to get back to customers quicker, which helps us with faster sales cycles. Our engineers and I have saved 100+ work hours since we started with Workstreet.


Start Your NIST 800-53 Program
Get a personalized roadmap based on your required baseline and current security posture.

From Baseline to Assessment-Ready
We cover NIST 800-53 from control selection to documentation, evidence and continuous monitoring.

Scoping & Baseline Selection

Gap Assessment

Control Implementation

Assessment & Monitoring
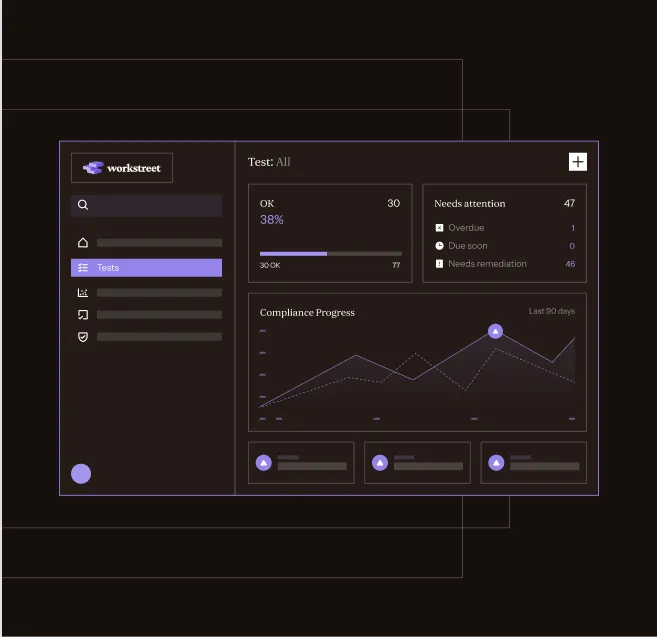
Step-by-step guidance for implementing and maintaining NIST 800-53 controls.
SOC 2 vs. NIST: What's the Difference?
Compare SOC 2 and NIST frameworks and decide which ones your customers and contracts require.
How Teams Run NIST-Aligned Security Programs
Real examples of companies that rely on Workstreet for NIST 800-53

From Compliance Burden to Strategic Advantage: How Workstreet Transformed Stride Health's Security Program
Stride Health, a leading cloud-based healthcare software company, partnered with Workstreet to transform their security and compliance program from a resource-intensive burden into a strategic business advantage. Over two years, Workstreet delivered exceptional results: 90% reduction in audit findings, 95% reduction in internal team time commitment, and zero findings in the latest penetration test—all while maintaining full HIPAA and NIST 800-53 compliance.
Clay's Path to ISO 42001 Certification
How an AI-native company used by 500,000+ teams built AI governance buyers can trust.
NIST 800-53 FAQs
Common questions about NIST 800-53 compliance
Federal agencies must apply NIST SP 800-53 controls to federal information systems under FISMA. Contractors and cloud providers that run systems for agencies are often required to meet it through contracts or FedRAMP. Many commercial organizations also adopt it voluntarily as a comprehensive control catalog.
NIST SP 800-53B defines Low, Moderate and High security control baselines, plus a privacy baseline. A system's baseline follows from its impact level under FIPS 199 and is then tailored to the environment. We help you select and tailor the right baseline before any control work starts.
No. NIST does not certify organizations against 800-53. Compliance is shown through control assessments, typically using the procedures in NIST SP 800-53A, and through decisions such as an agency authorization to operate or a FedRAMP certification. We get your evidence ready for that review.
NIST 800-53 is the full control catalog for federal systems. NIST 800-171 is a smaller set of requirements for protecting CUI in nonfederal systems and underpins CMMC Level 2. NIST CSF is a higher-level, outcome-based framework that any organization can use to manage cybersecurity risk.
Revision 5 is current. NIST issued Release 5.2.0 in August 2025, adding controls focused on secure software updates and patching. Your contracts or authorizing agency may name a specific release, so we confirm what applies to you and track updates so your program stays current.
Make NIST 800-53 Manageable
Get expert NIST 800-53 guidance that builds the right controls without burying your team in documentation.